- Compare Editions
- Product Information
- Resources
- Licensing / Pricing
- Support
- Contact

Making sure that only safe and vetted applications run is one of the best ways to secure servers and end-used computers from many kinds of malware. This feature is sometimes called application whitelisting, application allow listing or even application locker. We call it Trusted Applications.
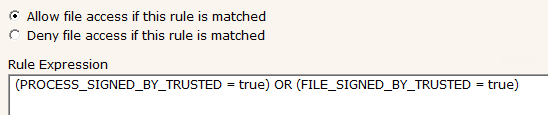
With the Trusted Applications feature, you define rules about which processes can be run, by whom, and even which files can be read by those applications (to optionally allow scripts to run in very specific situations you might have).
The rules can take into account the following characteristics:
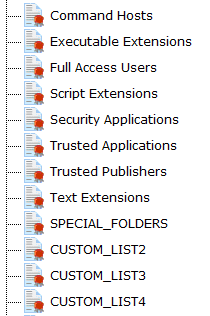
The rules are easy to write because they can refer to various lists of files, folders, product companies (application signers), users, etc. Just a few rules can quickly create a large amount of safety for many systems.
Handling the exceptional cases is easy too (example: it's simple to add the one-off application that needs to run in the Finance department).
Trusted Applications rules can be used on servers, as well as client computers via the optional Endpoint.
You could create rules like the following examples:
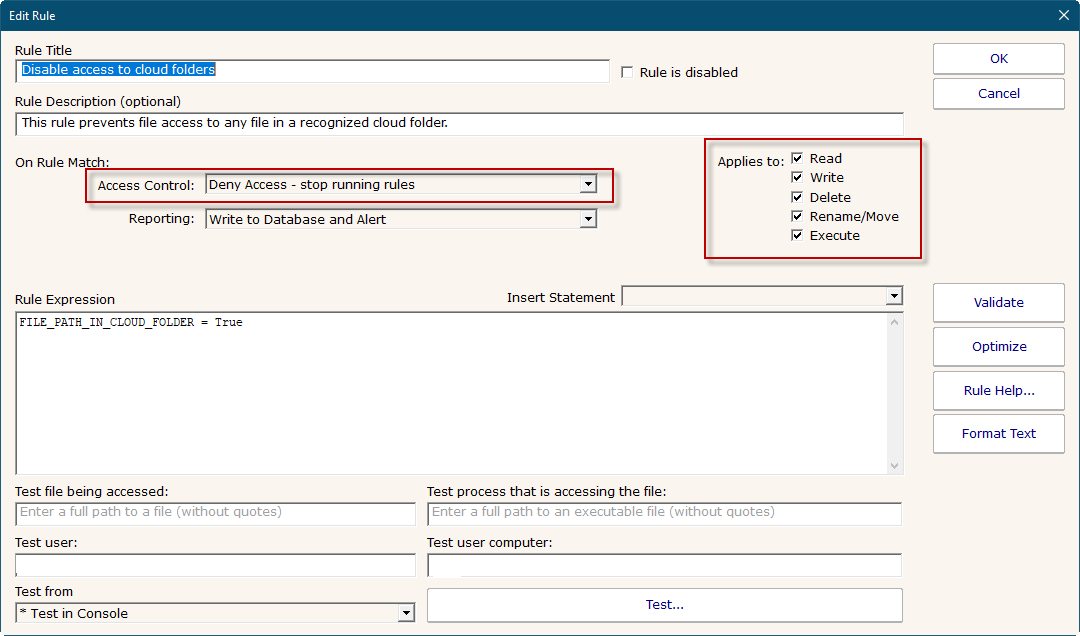
See some default rules below to see how easy they are to define:
The FILE_PATH_IN_CLOUD_FOLDER statement makes it very easy to block files from being written to cloud drives, and it can even prevent files from being read from a cloud drive.
“I'm working in this industry for 15 years now, but I can hardly remember working with a software company with a support like you have. You listen and new features come really fast. I'm deeply impressed by your support and now have the feeling we made the 100% right choice to choose PA Server Monitor.”
Hanjo P., Pohlmann & Dimai GbR, Germany